
Investors and partners
The keys are on a phone you already own.
AirNox is a self-custody wallet built on one assumption: the computer is already compromised. This page is a short briefing for investors and partners.
The problem
Where the money leaves
Keys on connected devices
Most thefts start on an ordinary computer, because that is where the key lives.
Tampered devices
A dedicated signing device can be opened and modified anywhere between the factory and the buyer's desk.
Blind signing, swapped addresses
People approve what they cannot read, and recipient addresses get swapped or poisoned.
What we built
A wallet that works around the weakest machine
Three hops. Keys at only one of them, and that one is offline.
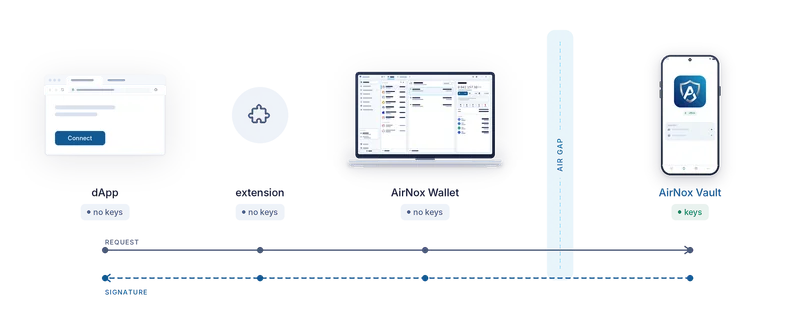
AirNox Wallet and AirNox Vault
A native desktop wallet, and an open-source app that turns any Android phone into an offline signer.
Read: Assume the computer is compromisedMass Adoption Security
Three ways across the gap
QR codes, Bluetooth LE and NFC, all carrying the same end-to-end encrypted, mutually authenticated session.
Read: Three ways across the gapThe transport is never trusted
Decoded signing
The phone parses each request from the bytes it will sign. Look-alikes and risky parameters become findings you must acknowledge.
Read: What the phone shows you
An MCP server with rules
AI agents act under a default-deny policy with fiat limits and an audit log.
Read: An MCP server with rules
dApps through a keyless extension
EIP-1193 and EIP-6963 for EVM networks, TON Connect, and the Solana and Sui wallet standards.
Swaps and bridges inside the wallet
Swaps with ranked quotes and bridges that recover, across 24 mainnets in six families: Bitcoin, TRON, Solana, Sui, TON and 19 EVM networks.
Market and losses
The numbers, with their sources
Third-party figures, checked on 13 October 2026 and rechecked on the day of publication.
| Metric | Figure | Period | Source |
|---|---|---|---|
| Crypto owners worldwide | 774M (estimate) | Jun 2026 | Crypto.com Research |
| Stolen in hacks per year | $1.7B (2023), $2.2B (2024), over $3.4B (2025) | 2023 to 2025 | ChainalysisSecurityWeek (2023) |
| Stolen in hacks, 2026 so far | about $2.7B to end of September (CertiK); $972M in H1 and about $1.73B to early September (TRM Labs) | 2026 | TRM Labs (H1)TRM Labs (to September)CertiK (Q3, via Yahoo Finance) |
| Private key, seed or infrastructure compromise | about 76% of losses | H1 2026 | TRM Labs |
| Personal wallets | $713M, about 80,000 victims | 2025 | Chainalysis |
| Drainer phishing (malicious signatures) | $83.85M, 106,106 victims | 2025 | ScamSniffer |
| Address poisoning | at least $83.8M lost; 270M attempts | Jul 2022 to Jun 2024 | USENIX Security 2025 |
| Tampered devices in the supply chain | reported losses above $86M; scope still developing | Oct 2026 | Industry press reports |
Firms count differently, and one 2025 incident dominates that year's total. Losses at exchanges, bridges and protocols, most of the value stolen in 2026, are outside what a self-custody wallet protects.
Opportunity and partners
Security without a hardware purchase
Any phone from any shop becomes the signer, so there is no device to buy and no shelf to tamper with.
Where it fits
Hardened phones
GrapheneOS is supported. AirNox Vault runs with or without Google services, on stock Android or a hardened build.
Terminals and kiosks
AirNox Wallet is native C++ and Qt, with no JavaScript runtime. Besides Windows, Linux and macOS, it runs on Raspberry Pi class hardware for terminals and kiosks.
DEX and dApp front ends
A front end connects through the standard wallet interfaces it already supports. In AirGap mode the user reads the decoded request on the phone before anything is signed.
Contact
Talk to the team
Details on request. Meet the team.
Wording to be approved This page is not an offer of securities. Figures are third-party and dated.
Join the waitlist
Leave your email and we will send release news. Nothing else.